Skip to content
  • 0 Votes
    1 Posts
    0 Views
    pitrh@mastodon.socialP
    EuroBSDCon 2026 talks online https://undeadly.org/cgi?action=article;sid=20260916093106 #openbsd #eurobsdcon #conference #development #security
  • 0 Votes
    2 Posts
    0 Views
    peteorrall@mastodon.bsd.cafeP
    @stefano Dear gods that list is huge.
  • Interesting links of the week:

    World security research
    1
    0 Votes
    1 Posts
    0 Views
    timb_machine@infosec.exchangeT
    Interesting links of the week:Strategy:* https://assets.publishing.service.gov.uk/media/6a50d66b1228eb26a4cab76c/National_Risk_Register_2026.pdf - I rave about the HMG risk register but it's a new year and there is still much to worry about* https://www.whitehouse.gov/wp-content/uploads/2026/08/NSSTS-082026.pdf - the US strategy for tech supremacy* https://www.wired.com/story/silicon-valley-doesnt-get-why-you-hate-ai/ - @WIRED makes some great points on AI scepticism* https://codeberg.org/ethical-foss/open-slopware#operating-systems - slop free software!* https://ar.al/2025/06/25/web-numbers/ - @aral writes small...* https://www.linkedin.com/pulse/i-spent-day-learning-wargaming-ive-stopped-thinking-since-nicholls-0wh8e - making incident exercises fun* https://home.treasury.gov/news/press-releases/sb0616/ - the US continues their great policy of going after activists* https://web.archive.org/web/20260828071449/https://cavallette.noblogs.org/2026/08/10083/2 - who exactly are noblogs and why you should care...* https://simonwillison.net/2026/Aug/28/just-a-rumour-of-a-bug/ - more thoughts on bugs * https://www.csis.org/analysis/cyberattacks-us-water-sector-and-iran-question-escalation-or-opportunism - more reporting on rain* https://www.whitehouse.gov/presidential-actions/2026/08/declaring-a-national-emergency-to-secure-the-united-states-bulk-power-system/ - once you've secured water, BES is next* https://www.cyber.gc.ca/en/news-events/joint-guidance-isolating-vital-systems - put your OT in a box say ASD and CCCS* https://www.ncsc.gov.uk/blogs/managing-the-cyber-risk-of-agentic-ai - NCSC drops some guidance on agentic AI * https://www.gov.uk/government/statistics/uk-public-survey-of-risk-perception-resilience-and-preparedness-2026 - HMG's report on public perception of risk, resilience and preparedness* https://ieeexplore.ieee.org/document/11644378 - paper on UK NIS readiness* https://blog.cryptographyengineering.com/2026/08/14/everything-is-about-to-go-dark/ - having spent years, presumably improving encryption, @matthew_d_green is worried that threat actors may go dark* https://www.cyberleagle.com/2026/08/if-computer-is-not-accountable-who-is.html - @cyberleagle.bsky.social asks the awkward question, "who do we prosecute?"Standards:* https://www.etsi.org/newsroom/press-releases/etsi-launches-approval-process-for-17-european-standards-supporting-the-cyber-resilience-act/ - new ETSI standards, in support of EU CRAThreats:* https://www.fortinet.com/blog/threat-research/multi-functional-linux-botnet-evooo1bot - another day, another botnet* https://securelist.com/honeymyte-coolclient-driver-rootkit/ - another day, another rootkit from @Kaspersky* https://blog.talosintelligence.com/uat-10147-deploys-spectre-a-cross-platform-implant-with-linux-rootkit-and-byovd-capabilities/ - another one for luck, this time from my friends at @TalosSecurity* https://citizenlab.ca/research/uncovering-global-telecom-exploitation-by-covert-surveillance-actors/ - @citizenlab reporting on global surveillance* https://www.mdsec.co.uk/2026/08/when-it-snows-it-pours-anatomy-of-a-servicenow-red-team/ - more from MDSec on SNow* https://insights.bridewell.com/hubfs/Reports/Defending%20Against%20DPRK%20IT%20Workers%20-%20An%20Implementation%20and%20Operational%20Guide.pdf - what to do to avoid meeting a .kp colleague at the water coolerDetection:* https://www.cisa.gov/news-events/cybersecurity-advisories/aa26-237a - SOC lessons from CISA* https://maldbg.com/interlock-esxi-decryptor-internals - don't pay the ransom* https://techcrunch.com/2026/08/19/t-mobile-chopped-a-cable-to-expel-chinese-hackers-from-its-network/ - scissors are essential for DFIR* https://www.elastic.co/security-labs/ai-coding-agent-audit-cursor-hooks - if you don't fully trust your AI, how do you keep an eye on it?Bugs:* https://minanagehsalalma.github.io/zyxel-social-login-bypass-cve-2026-8508/ - too social network* https://www.usenix.org/system/files/usenixsecurity26-kim-daewoo.pdf - side channels in vSwitch* https://labs.watchtowr.com/youre-back-in-the-room-citrix-netscaler-pre-auth-rce-cve-2026-8452/ - are the NetScalers still in the room @index?Exploitation:* https://cdn.openai.com/pdf/67869394-cb91-4c12-888c-5cbd85c7814c/OpenAI-Hugging-Face%20Incident-Technical-Report.pdf - so, nothing that clever then... * https://tmpout.sh/5/ - new @tmpout* https://exploitation.ashemery.com/ - a nice little course on exploitation* https://www.akamai.com/blog/security-research/bring-your-own-edr-turn-commercial-edr-trojan-horse - replicating CrowdStrike's excellent work on turning EDR into a footgun* https://smolbox.remyhax.xyz/ - why not play with AI in someone else's container? Hard hacks:* https://boschko.ca/g1-ble-rce/ - thank @boschko, for when the robots rise...* https://blog.n0p.me/2026/08/2026-08-21-fortitool-fortios-decryption/ - dump FortiOS* https://www.usenix.org/conference/usenixsecurity26/presentation/anwar - who cares what the date is...* https://0x434b.dev/breaking-secure-boot-without-breaking-the-crypto/ - untrusted boot from @434bData:* https://datarepublican.com/dsa-explorer/ - if you're in the US, what data are they keeping on you? Nerd:* https://lists.debian.org/debian-vote/2026/08/msg00360.html - @debian sadness * https://littlefedi.org/ - @stefano's bit of the Fediverse* https://eater.net/ - a little bit of light CPU design, just for fun!#security, #research
  • 0 Votes
    1 Posts
    0 Views
    dkade@mastodon.bsd.cafeD
    And now something different, recovering and "old" laptop. https://dkade.com/posts/lenovo_t540p_bios_unlock/#hacking #electronics #security
  • 0 Votes
    1 Posts
    0 Views
    mboelen@mastodon.socialM
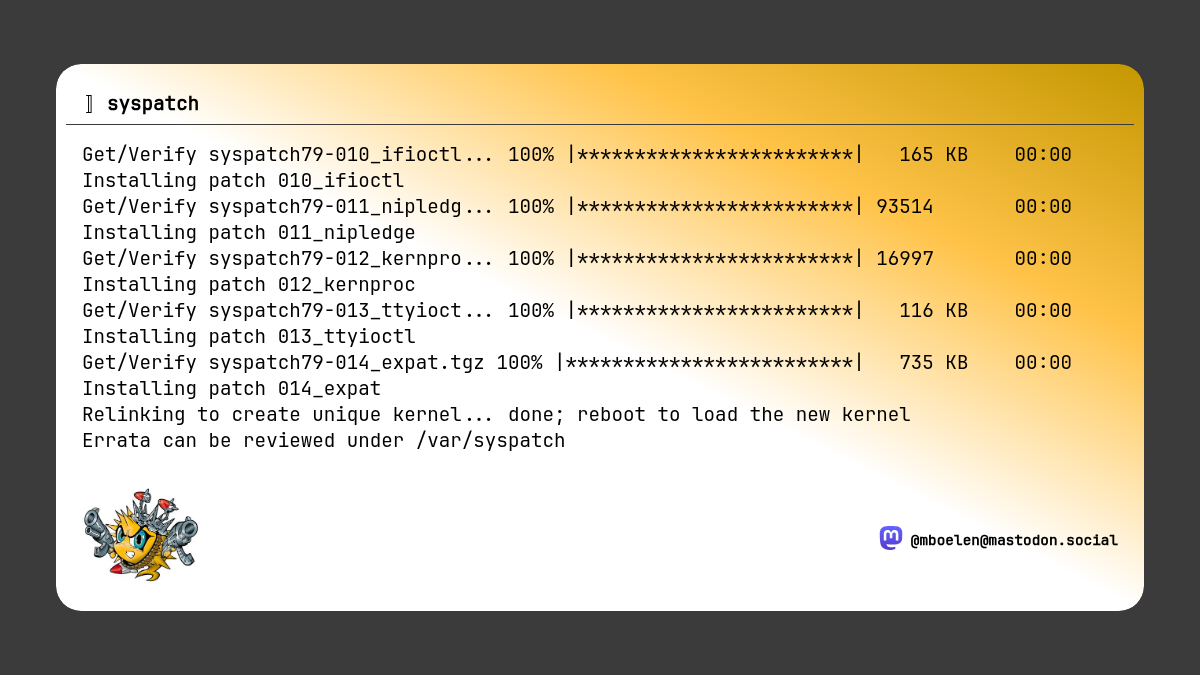
    I think #OpenBSD has one of the easiest methods to update (important) system updates. Just run syspatch and reboot.Simplicity has many benefits and I think OpenBSD is one that clearly shows this.#OpenBSD #systemadministration #security
  • 0 Votes
    1 Posts
    99 Views
    grahamperrinG
    https://daniel.haxx.se/blog/2026/04/22/high-quality-chaos/ via https://mastodon.social/@bagder/116448188069484288 (2026-04-22) – not recent, but it's news to me. From today's post about last month's Ottawa FreeBSD Developer Summit: Michael Winser – Alpha Omega – The Changing Landscape of Open Source Software Security AI has entered the chat A frame from Winser's presentation: [image: 1785197784883-9a762f41-ee1e-471a-9e56-b4100b9d01a5-image.jpeg] Daniel Stenberg on AI in security ― sentiment over time From Stenberg's blog post: … Everything is AI now Almost every security report now uses AI to various degrees. You can tell by the way they are worded, how the report is phrased and also by the fact that they now easily get very detailed duplicates in ways that can’t be done had they been written by humans. The difference now compared to before however, is that they are mostly very high quality. The reporters rarely mention exactly which AI tool or model they used (and really, we don’t care), but the evidence is strong that they used such help. We are not unique I did a quick unscientific poll on Mastodon to see if other Open Source projects see the same trends and man, do they! Friends from the following projects confirmed that they too see this trend. … Additional tag: AI ― #ai is currently not possible in (NodeBB) BSD Cafe Billboard.
  • Torvalds attacks IT industry 'security circus'

    World linux openbsd security
    1
    0 Votes
    1 Posts
    80 Views
    CiotBSDC
    Linux creator calls OpenBSD crowd a bunch of "monkeys" and criticizes those who publicize security flaws to gain notoriety. https://www.cnet.com/tech/tech-industry/torvalds-attacks-it-industry-security-circus-1/
  • 1 Votes
    1 Posts
    234 Views
    grahamperrinG
    https://freebsdfoundation.org/blog/freebsd-ai-assisted-vulnerability-discovery-project-launch/ … the key goal of reducing the number of exploitable vulnerabilities in the FreeBSD source code. The 6-month project is being funded by a grant from the Alpha Omega project. The funds will be used to engage FreeBSD Security Team members under fixed-term contracts to find and patch vulnerabilities. The Security Team’s access to publicly available AI models and tokens will be provided free of charge. AI will be used for vulnerability discovery and analysis only, all patches will be manually created. … In GitHub: all-projects/AI-assisted-vulnerability-discovery at main · FreeBSDFoundation/all-projects FreeBSD Receives Funding To Launch AI-Assisted Vulnerability Discovery - Phoronix discussion via https://fosstodon.org/@governa/116755744623083032 @governa@fosstodon.org FreeBSD AI-assisted Vulnerability Discovery Project launch | The FreeBSD Forums Cross-posted to r/freebsd in Reddit.
  • 1 Votes
    1 Posts
    160 Views
    grahamperrinG
    https://www.blackduck.com/content/dam/black-duck/en-us/reports/rep-ossra.pdf The “Open Source Security and Risk Analysis” (OSSRA) report has been the industry’s definitive look at the state of open source code for a decade. Each year, we analyze anonymized findings from commercial codebases audited by the Black Duck Audit Services team, and this provides an unmatched, real-world view of how open source is used—and sometimes misused—across every major industry. This year’s findings document a pivotal moment: The explosion of AI-assisted development has fundamentally altered the risk landscape for software and the baseline for compliance with new regulatory initiatives such as the EU Cyber Resilience Act (CRA) and the Digital Operational Resilience Act (DORA). PDF, 44 pages. Context Open source organisations weigh in on age attestation Availability Noted in Reddit: … easily found with Google – without completing Black Duck's form, which requires a business email address: https://www.google.com/search?q="2026+Open+Source+Security+and+Risk+Analysis+Report"+PDF&udm=14 …
  • [vez.mrks.md]

    FreeBSD freebsd security hardening
    6
    -1 Votes
    6 Posts
    602 Views
    CiotBSDC
    No problem with the vote @grahamperrin said: For what it's worth, I think: don't delete it from BSD Cafe Billboard. It's good to raise awareness of the reputation. I hadn't thought of it that way. Interesting!
  • 0 Votes
    1 Posts
    114 Views
    CiotBSDC
    In the world of open source, trust is our most valuable currency. ONAP is a “collection of individual, semi-standalone network automation functions that provide design, orchestration, observability, and automation of network and edge services for operators, cloud providers, and enterprises” (per ONAP). When we build software that powers global telecommunications, “good enough” isn’t an option… https://openssf.org/blog/2026/05/07/the-road-to-gold-how-cps-set-a-new-standard-for-security-and-quality-in-open-source/
  • 2 Votes
    1 Posts
    146 Views
    CiotBSDC
    ⇒ Open Infrastructure is Not Free: A Joint Statement on Sustainable Stewardship (2025/09/23) An Open Letter from the Stewards of Public Open Source Infrastructure Over the past two decades, open source has revolutionized the way software is developed. Every modern application, whether written in Java, JavaScript, Python, Rust, PHP, or beyond, depends on public package registries like Maven Central, PyPI, crates.io, Packagist and open-vsx to retrieve, share, and validate dependencies. These registries have become foundational digital infrastructure – not just for open source, but for the global software supply chain… https://openssf.org/blog/2025/09/23/open-infrastructure-is-not-free-a-joint-statement-on-sustainable-stewardship/ ⇒ Open Infrastructure Is Not Free, Part II: The Hidden Cost of Running Package Registries (2026/05/06) The September 2025 Working Together Towards Sustainable Open Source open letter raised the alarm about the economic sustainability of open source package registries, highlighting how rising adoption and the pace of innovation are placing new and growing pressures on open source package registries. Those pressures have only accelerated in the time since the letter, amplified by the adoption of AI coding agents and tools… https://openssf.org/blog/2026/05/06/open-infrastructure-is-not-free-part-ii-the-hidden-cost-of-running-package-registries/
  • 2 Votes
    1 Posts
    243 Views
    grahamperrinG
    https://www.daemonology.net/blog/2026-04-11-20-years-on-AWS-and-never-not-my-job.html I created my first AWS account at 10:31 PM on April 10th, 2006. I had seen the announcement of Amazon S3 and had been thinking vaguely about the problem of secure backups — even though I didn't start Tarsnap until several months later — and the idea of an online storage service appealed to me. The fact that it was a web service made it even more appealing; I had been building web services since 1998, … – 24–30 minutes reading time, according to Firefox. Time well spent, IMHO, especially with security vulnerabilities for various operating systems recently in a spotlight. Also: to Mastodon @cperciva@mastodon.social @stefano and to Lobsters. Background: Colin Percival was, for many years, the FreeBSD Security Officer. He is now the FreeBSD Release Engineering Lead. You can show your appreciation for today's blog post at his shares in Reddit, in Hacker News, or in LinkedIn. A thought: AWS has its heroes. Tarsnap has given 2^18 dollars to open source – for this, and for what's described in today's blog post, it's probably fair to describe Colin as a hero in more ways than one.
  • 1 Votes
    2 Posts
    197 Views
    grahamperrinG
    For convenience, from the toot in Mastodon: https://www.reddit.com/r/freebsd/comments/1sgmi14/claude_mythos_preview_fully_autonomously_finds/ … (plus Linux, OpenBSD, and others) – more concerning than calif.io story with known CVE and human prompting? …" – @bigsneakyduck (Sorry. I imagined that the original mention in Mastodon would have shared the whole of the toot as the opening post here.)