Skip to content

OpenBSD

58 Topics 169 Posts

Strong, secure, no compromises.
For all things OpenBSD, pf, and pledge.

This category can be followed from the open social web via the handle openbsd@billboard.bsd.cafe

  • Welcome to the OpenBSD Section

    Pinned
    1
    3 Votes
    1 Posts
    411 Views
    stefanoS
    Secure by default, no compromises. Discuss anything related to OpenBSD here: pf, pledge, unveil, httpd, relayd, installations, hardware support, or just why you chose OpenBSD and never looked back. Whether you run it as your daily driver or as the silent guardian of your network, this is your table.
  • Hyprland on OpenBSD

    1
    2 Votes
    1 Posts
    72 Views
    CiotBSDC
    26/11/04 ⇒ Hyprland is now available on OpenBSD Yes, it’s strange, it’s crazy, yes - it used to be impossible. But the time has come when Wayland on OpenBSD has matured enough to run massive and beautiful compositors. https://nazarenko.sbs/hyprland-is-now-on-openbsd/
  • [Poolp.org] Gilles Chehade

    1
    0 Votes
    1 Posts
    70 Views
    CiotBSDC
    26/10/31 ⇒ OpenBSD 8.0 on a Scaleway Instance Every few years I want to install OpenBSD at Scaleway… but they don’t support OpenBSD and I need to find a way to install regardless. https://poolp.org/posts/2026-10-31/openbsd-8.0-on-a-scaleway-instance/
  • [Undeadly.org] OpenBSD logs

    openbsd packetfilter tables
    13
    3 Votes
    13 Posts
    855 Views
    CiotBSDC
    26/11/06 ⇒ OpenBSD top(1) adds flag to show chroot, pledge and unveil status With one recent commit, the top(1) command on OpenBSD became quite a bit more useful. The commit adds a new -Q flag to show each process' use of the chroot(2), pledge(2) and unveil(2) facilities. https://undeadly.org/cgi?action=article;sid=20261106104957
  • [FuguIta]

    1
    1 Votes
    1 Posts
    83 Views
    CiotBSDC
    26/10/25 ⇒ FuguIta 8.0 https://fuguita.org/?FuguIta/8.0
  • OpenBSD Webzine

    1
    2 Votes
    1 Posts
    162 Views
    CiotBSDC
    26/10/20 ⇒ OpenBSD Webzine ISSUE #20 OpenBSD 8.0 released! https://webzine.puffy.cafe/issue-20.html https://webzine.puffy.cafe/fr_issue-20.html (French version)
  • Force fsck on reboot

    openbsd fsck runbsd
    4
    6 Votes
    4 Posts
    149 Views
    andersgoA
    Speak of the devil - AI makes it irresponsible to keep an uptime on any prod systems for more than a week nowadays. Hope there will come something good out in the end "0 days without 0 day..."
  • Fabricati-diem

    1
    1 Votes
    1 Posts
    116 Views
    CiotBSDC
    26/09/13 ⇒ Deshittification as a Service: Reclaiming Privacy and Performance with OpenBSD pf and Unbound When you buy a modern Smart TV, you are buying a display subsidized by surveillance. Even at high price points, manufacturers make slim margins on physical hardware. To drive post-sale revenue, they track your viewing habits, log your interactions, and serve you targeted ads. Smart TVs, especially LG models running WebOS, have quietly morphed from simple screens into active network spyware appliances. https://fabricati-diem.inform.social/post/deshittification-as-a-service/ 26/09/20 ⇒ Deshittification Part 2: Bypassing the App Store Gatekeeper In my previous post, Deshittification as a Service, I shared a blueprint for taking back control from modern Smart TVs. I placed an LG OLED running WebOS inside an isolated VLAN behind an OpenBSD gateway. My goal was simple. I wanted to block vendor telemetry, strip out ads, and force the TV to act like a plain display again. ⇒ Deshittification Part 3: The Cold-Boot Consent Trap in Three Acts In my first write-up, Deshittification as a Service, I laid out a network blueprint using OpenBSD, pf and Unbound to isolate an LG Smart TV running WebOS inside a dedicated VLAN. In Part 2: Bypassing the App Store Gatekeeper, I documented how WebOS responds to telemetry blocking by locking users out of the LG Content Store with artificial error codes, effectively holding software management hostage. https://fabricati-diem.inform.social/post/deshittification-as-a-service-part3-the-cold-boot-consent-trap-in-three-acts/ 26/10/04 ⇒ Deshittification Part 4: The Factory Reset Consent Trap In Part 1 of this series, I laid out the foundational OpenBSD and Unbound architecture used to reclaim network sovereignty from an LG Smart TV. In Part 2, we saw how the OS holds the App Store hostage. In Part 3, I documented a stateful TCP kill switch that actively terminates Netflix streams if telemetry is blocked. https://fabricati-diem.inform.social/post/deshittification-as-a-service-part4-the-factory-reset-privacy-trap/
  • [Rafael Sadowski: rsadowski.de]

    2
    0 Votes
    2 Posts
    203 Views
    CiotBSDC
    26/10/02 ⇒ Headers Up! What's New in httpd and relayd As I mentioned in my Dead Software Walking: The ongoing evolution of relayd(8) and httpd(8) post, development of relayd(8) and httpd(8) was revived. https://rsadowski.de/posts/2026/update-relayd-and-httpd/
  • [T.I.S: Tech Idea Systems (Blog & Ideas)]

    1
    1 Votes
    1 Posts
    128 Views
    CiotBSDC
    26/09/18 ⇒ Website Migration To OpenBSD! I had an issue with my previous webserver running Arch Linux where my SSH private key suddenly disappeared from the machine. I'm not sure whether it was due to the OpenSSH update from the prior day or a hack, but I wasn't too keen to find out. The main issue I had with running Arch Linux as a webserver was surrounding the replacement of cron with systemd timer files which I found really annoying to use. I personally don't get why the developers chose to replace a solid well-known tool that is simple to use with a tool that has so much complexity to it. https://tech-idea.systems/blog-posts/webserver-migration.html
  • [Nemin's Blog]

    1
    1 Votes
    1 Posts
    101 Views
    CiotBSDC
    26/09/13 ⇒ Tunnelling SSH over WireGuard on OpenBSD Making your access logs cleaner by restricting who can connect to your VPS https://nemin.hu/wireguard-ssh/index.html
  • OpenBSD VPS for $5 a Year

    1
    3 Votes
    1 Posts
    99 Views
    CiotBSDC
    A guide to deploying an OpenBSD VPS on TierHive, a NAT VPS provider offering supported OpenBSD images for under $5 per year. It covers setting up a 512 MB instance, SSH keys, and routing domain traffic with SSL using TierHive's built-in HAProxy service. https://btxx.org/posts/cheap-openbsd-vps/
  • [Miod Vallat] OpenBSD stories

    openbsd zaurus
    8
    5 Votes
    8 Posts
    742 Views
    CiotBSDC
    26/09/02 ⇒ OpenBSD stories—Strange Medieval Devices In the late 1970s and the 1980s, the best choice for high-performance, high-capacity storage was so-called SMD disks. http://miod.online.fr/software/openbsd/stories/smd.html
  • [Dr Brian R. Callahan]

    openbsd antirop
    2
    1 Votes
    2 Posts
    270 Views
    CiotBSDC
    26/08/11 ⇒ Cleaning costs, or, examining the OpenBSD -fret-clean flag I start with apologies to williewillus, calvin, and reezer on Lobste.rs. Prior to July 9, I would have agreed with you all. But it appears I was wrong. There is no need to further engage; it is clear that critique-from-within is undesirable. Which is perfectly OK, because I stepped away from being on the inside. So let's just keep evaluating OpenBSD's mitigations and we'll continue to learn interesting things along the way. https://briancallahan.net/blog/20260811.html
  • OpenBSD in the wild... spotted at the gym

    8
    2
    3 Votes
    8 Posts
    321 Views
    naltunN
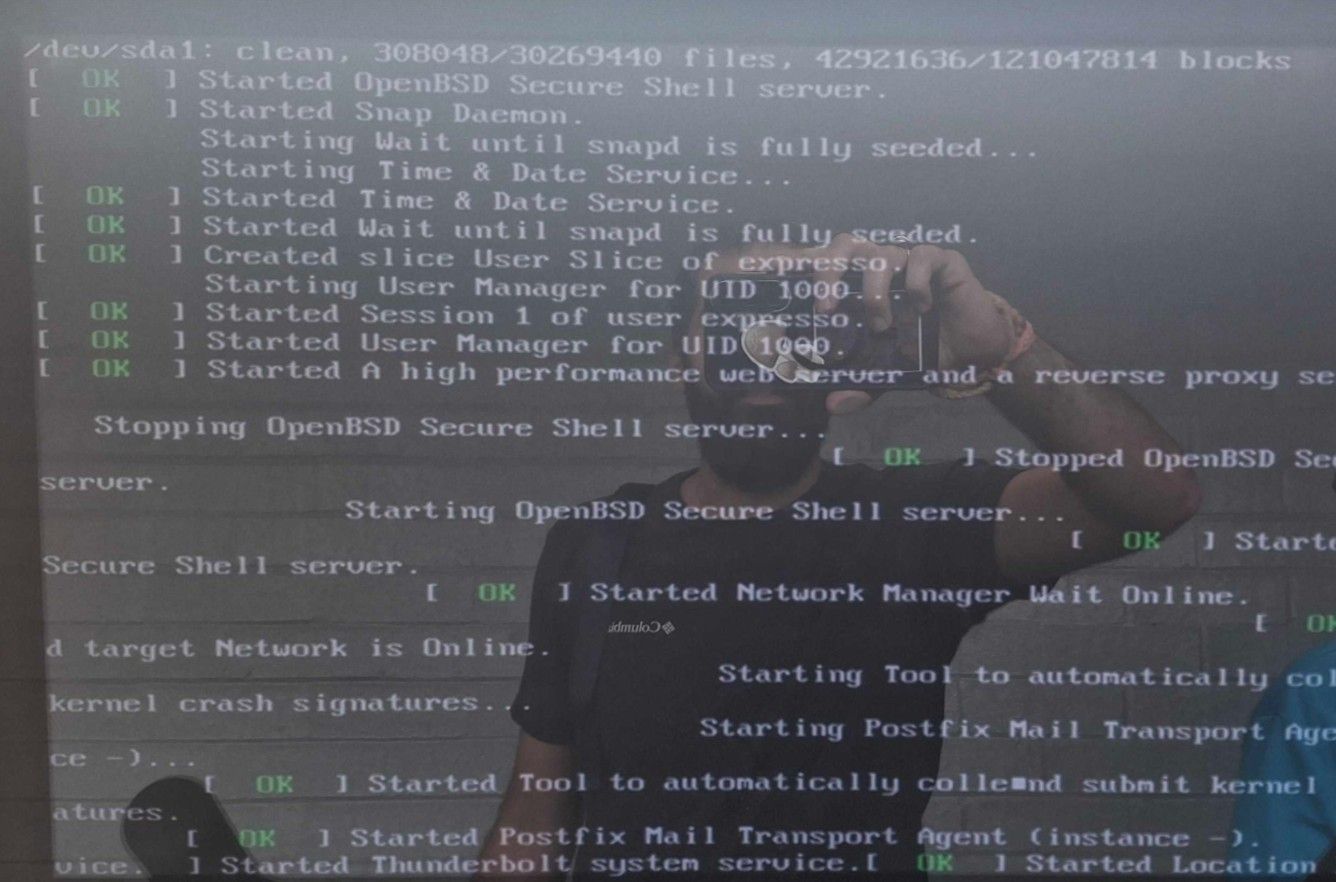
    Thanks to everyone who pointed out Linux. Now that I'm paying attention this is clearly the systemd startup logging.
  • wg(4), pf(4), and relayd(8): a love story

    1
    2 Votes
    1 Posts
    135 Views
    naltunN
    tl;dr I used wg(4), pf(4), and relayd(8), all OpenBSD native tools, to encrypt all inbound connections from a gateway VPS to my local home server. This also hides my local IP information and I managed it all without much hassle and pain. I recently stood up a VPS running OpenBSD 7.9 on Vultr. The VPS is hosted in Chicago, Illinois, USA. I then took OpenBSD's native WireGuard driver, wg(4), to establish an encrypted tunnel to my local home lab server. Using relayd(8), OpenBSD's native reverse proxy, I can now forward virtual host connections to my home lab server, which has httpd(8) as a web server frontend. I used pf.conf(5) to configure OpenBSD's native fireweall, pf(4), which was incredibly easy. The result is a secure gateway that routes all traffic via WireGuard to my local server, obfuscating its location and other IP information. This was done by simply configuring handful of system daemons. I've done some OpenBSD network configuration before, but this was the most work I've done. The best part, it wasn't that difficult, and all manual pages provided sufficient details to work with them. Once I get my site set up I'll write up the experience and step-by-step instructions and share the page here. New OpenBSD milestone unlocked; no intent to stop anytime soon Happy hacking, hackers!
  • [Arxiv.org]

    openbsd study measures
    2
    0 Votes
    2 Posts
    237 Views
    grahamperrin@mastodon.bsd.cafeG
    @phessler FYI
  • [dataswamp.org/~solene] Full-featured email server running OpenBSD

    4
    1 Votes
    4 Posts
    281 Views
    CiotBSDC
    @naltun said: tyvm ??? Hummm, maybe: "Thank you very much", isn'it?!
  • 2 Votes
    1 Posts
    142 Views
    izder456I
    What title says More info here: https://github.com/outpaddling/desktop-installer/issues/30#issuecomment-4835472901
  • 2 Votes
    2 Posts
    319 Views
    CiotBSDC
    @grahamperrin said: OT ???